Share
EU's AI Act Implementation Rules Near Finalization: High-Risk AI Systems to Require Third-Party Compliance Assessments by CNIL/BSI, Chinese AI Exports Need Dual CE + AI Act Certification
Introduction
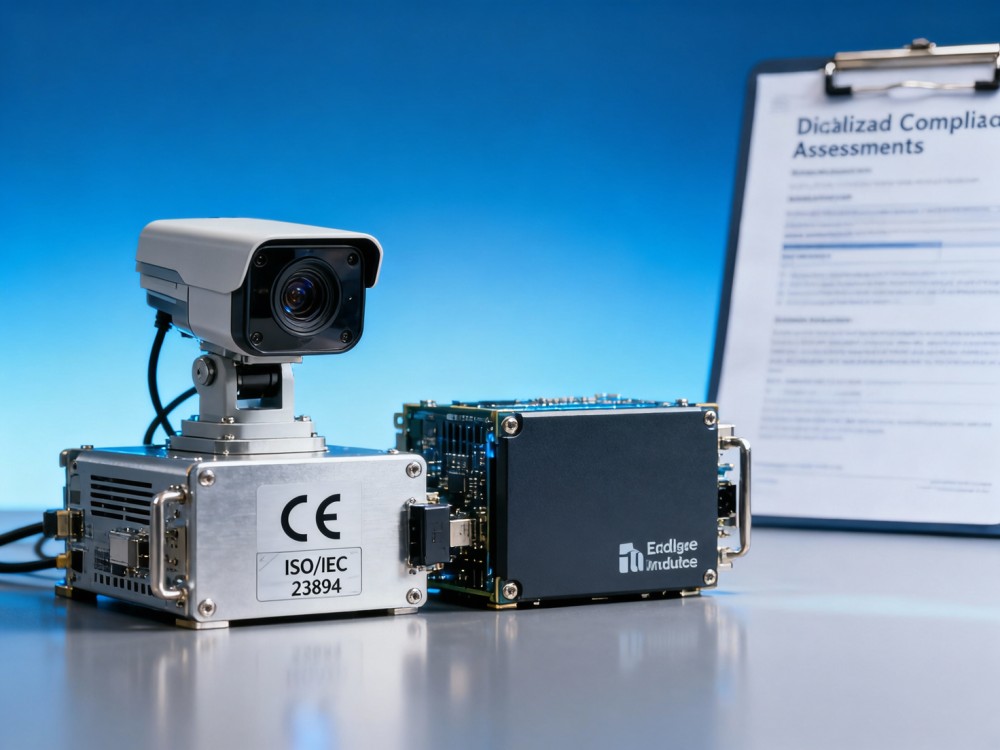
The European Commission announced on March 22, 2026, that the implementing regulations for the EU's AI Act will take effect in Q3 2026. High-risk AI systems, including intelligent surveillance equipment, industrial quality inspection software, and autonomous driving dispatch platforms, must undergo compliance assessments by authorized EU third-party bodies such as Germany's BSI and France's CNIL. This development is particularly critical for Chinese AI hardware manufacturers and SaaS providers, who must align with EN 301 549 and ISO/IEC 23894 standards to avoid market entry delays or bans. Industries involved in AI-driven automation, surveillance, and industrial applications should closely monitor these requirements.
Event Overview
The EU's AI Act supplementary implementation rules will officially come into force in Q3 2026. Confirmed details include:
- Mandatory third-party compliance assessments for high-risk AI systems entering the EU market.
- Authorized assessment bodies include Germany's Federal Office for Information Security (BSI) and France's National Commission on Informatics and Liberty (CNIL).
- Non-compliant AI products, particularly those lacking documentation aligned with EN 301 549 or ISO/IEC 23894, may face market access restrictions.
Impact on Key Industries
1. AI Hardware Manufacturers
Chinese exporters of AI-enabled surveillance cameras, robotics, and edge computing devices will need to undergo rigorous conformity assessments. The lack of pre-certified documentation may disrupt supply chains, particularly for OEM/ODM suppliers serving EU-based integrators.
2. Industrial AI Software Providers
SaaS platforms offering quality inspection, predictive maintenance, or automated scheduling must adapt their technical documentation. Industrial AI solutions without standardized risk-mitigation protocols may face longer approval cycles.
3. Autonomous Mobility Developers
Companies providing AI-driven fleet management or traffic control systems must prepare for BSI/CNIL audits. The requirement extends to both embedded vehicle systems and cloud-based dispatch platforms.
Key Action Points for Businesses
1. Prioritize Dual Certification Pathways
From an industry perspective, achieving CE marking alone will no longer suffice. Companies should initiate parallel compliance processes for both CE and AI Act requirements, particularly for products falling under Annex III high-risk categories.
2. Document Governance Frameworks
Current standards indicate that ISO/IEC 23894 (AI risk management) and EN 301 549 (digital accessibility) will form the baseline. Technical documentation should explicitly map AI system functionalities to these frameworks.
3. Engage Notified Bodies Early
Given potential bottlenecks at authorized assessment bodies like BSI, proactive engagement with conformity assessment specialists is advisable—especially for complex systems involving computer vision or machine learning components.
Editorial Perspective
Analysis suggests this development represents more than procedural updates—it signals the EU's hardening stance on algorithmic accountability. While the 2026 timeline allows for adaptation, the following aspects warrant attention:
- The practical challenges of harmonizing technical documentation across differing national interpretations by EU member states' designated bodies.
- Potential ripple effects as other jurisdictions (e.g., UK, Canada) may adopt similar third-party assessment models.
- The operational burden for SMEs lacking in-house compliance teams, possibly accelerating demand for AI governance consultancies.
Conclusion
The AI Act implementation rules crystallize the EU's risk-based regulatory approach, creating both compliance hurdles and opportunities for market differentiation. Enterprises should treat this as a strategic inflection point—beyond mere technical adjustments, it necessitates reevaluating product development lifecycles and post-market surveillance mechanisms. The immediate priority lies in gap analyses against EN/ISO standards while monitoring evolving guidance from notified bodies.
Sources
- European Commission Announcement (March 22, 2026)
- EN 301 549 Standard on Digital Accessibility
- ISO/IEC 23894 Guidelines on AI Risk Management
Ongoing developments regarding national competent authorities' designation procedures require further monitoring.
Policy & Regulations Desk
Related News
- 00
0000-00
What Consumer Electronics Policy Shifts Matter Most in 2026? - 00
0000-00
What the NIS2 directive changes for data security in Europe - 00
0000-00
EU Requires Digital CE Labels for Office Electronics - 00
0000-00
Supply Chain Services Compliance: Key Standards That Reduce Audit Risk - 00
0000-00
EU REACH SVHC Update Triggers August Filing for Office Electronics
Weekly Insights
Stay ahead with our curated technology reports delivered every Monday.