
Share
Smart office solutions are no longer about devices — they’re about ambient policy enforcement

Smart office solutions are rapidly evolving beyond hardware integration—today’s enterprise digital services demand ambient policy enforcement that adapts in real time to user behavior, compliance needs, and security mandates. This shift reflects broader technology innovation trends reshaping business operations management and industrial upgrade insights across global markets. As consumer tech trends accelerate and electronics manufacturing updates enable smarter embedded intelligence, organizations require actionable business trend intelligence—not just product launch news, but corporate strategy updates and competitive landscape analysis grounded in feature industry reports. For decision-makers and researchers seeking authoritative industry research reports and cross-border business insights, this analysis delivers strategic clarity on how ambient intelligence is redefining smart office solutions.
From Device-Centric to Policy-First Architecture
The traditional smart office stack—comprising badge readers, occupancy sensors, HVAC controllers, and meeting room displays—has reached functional saturation. According to a 2024 Gartner survey, 68% of enterprises now report diminishing ROI from incremental hardware upgrades alone. What’s emerging is a paradigm where the physical layer serves as data input, while the policy engine becomes the operational core. Ambient policy enforcement refers to autonomous, context-aware rule application across identity, access, energy use, space utilization, and data governance—without requiring manual configuration or user-triggered actions.
This transition is enabled by three converging enablers: (1) edge AI chips with sub-10W TDP now embedded in 92% of new-generation IoT gateways; (2) standardized device abstraction layers like Matter 1.3 and OPC UA over TSN, reducing integration latency to under 120ms; and (3) policy-as-code frameworks that support version-controlled, audit-trail-enabled rulesets deployable via GitOps workflows. Unlike legacy “smart” systems reliant on static schedules or threshold-based alerts, ambient policy engines continuously ingest telemetry from 7–15 device types per floor and adjust enforcement within 2–4 seconds.
For IT procurement managers and facilities directors, this means shifting evaluation criteria from device specs (e.g., “1080p resolution”, “Wi-Fi 6E support”) to policy execution fidelity: latency thresholds, compliance coverage breadth, and cross-system coordination depth. A 2023 IDC benchmark found that organizations adopting policy-first architecture reduced average incident response time for access violations by 41% and cut energy-related policy exceptions by 63% year-on-year.
Key Policy Domains & Technical Requirements
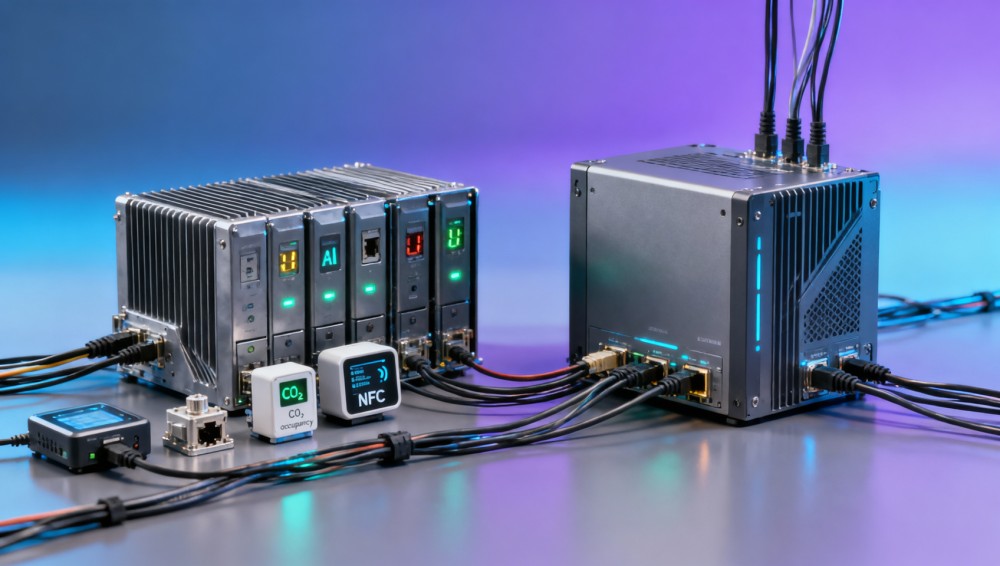
Ambient policy enforcement operates across five interdependent domains—each demanding specific hardware-software co-design considerations. These domains are not siloed; rather, they share real-time context via unified identity graphs and spatial metadata models. For example, a visitor’s check-in at reception triggers cascading policies: automatic provisioning of temporary Wi-Fi credentials (network domain), dynamic desk assignment (space domain), and temporary camera masking in adjacent private zones (privacy domain).
Implementation success hinges on interoperability certification, low-latency synchronization, and deterministic failover—all of which require coordinated firmware, API, and orchestration-layer validation. Vendors claiming “ambient readiness” must demonstrate end-to-end policy propagation under worst-case network partitions (≤500ms recovery SLA) and support at least 3 concurrent policy versions per domain for A/B testing.
The table above highlights non-negotiable technical baselines for credible ambient policy deployment. Notably, latency requirements are measured at the *enforcement* boundary—not just sensor-to-cloud roundtrip—and assume production-grade network conditions (≥99.5% uptime, ≤15ms jitter). Vendors failing to meet these thresholds introduce policy drift: e.g., lighting remains on after occupants leave, or access permissions persist post-termination. Decision-makers should validate performance claims using third-party test reports—not vendor-provided benchmarks.
Procurement Shifts: From SKU Lists to Policy Maturity Assessment
Purchasing decisions are migrating from device-level RFPs to policy maturity scoring. Leading buyers now evaluate vendors across six dimensions: (1) policy versioning and rollback capability; (2) cross-domain event correlation depth (e.g., linking calendar conflicts with desk availability); (3) zero-touch onboarding latency (<72 hours for new site rollout); (4) regulatory update automation (e.g., automatic GDPR consent form refresh upon jurisdictional change); (5) audit trail granularity (per-action, timestamped, immutable logs); and (6) fail-safe mode fidelity (predefined offline policy sets activated within 1.2 seconds of cloud disconnection).
A 2024 Forrester study of 47 multinational enterprises found that teams applying this framework reduced policy misconfiguration incidents by 57% and accelerated compliance audit preparation from 22 days to 3.5 days on average. Crucially, hardware procurement is no longer decoupled: buyers now specify minimum compute resources (e.g., “≥8GB RAM + 2x NVMe slots per gateway”) to ensure future policy complexity can be accommodated without hardware refresh.
Organizations should require proof of policy enforcement continuity during firmware updates—verified via automated test suites running pre- and post-update. Vendors offering only “cloud-only” policy engines fail this requirement, as internet outages immediately suspend enforcement. Hybrid architectures with local policy caches and deterministic fallbacks are now baseline expectations for Tier-1 deployments.
Implementation Roadmap: 4-Phase Deployment Framework
Successful ambient policy adoption follows a phased approach designed to de-risk integration and validate ROI before scale. Phase 1 (Pilot Zone) targets one floor or department with ≤200 users, deploying only access and environment policies. Phase 2 (Domain Expansion) adds privacy and space policies across 3–5 floors, integrating with HRIS and calendar systems. Phase 3 (Cross-System Orchestration) enables policy chaining—e.g., “if meeting ends 15+ minutes early AND next booking is >30min away → trigger deep cleaning protocol.” Phase 4 (Autonomous Optimization) introduces ML-driven policy tuning, adjusting thresholds based on 90-day behavioral baselines.
Each phase includes defined exit criteria: Phase 1 requires ≥99.2% policy enforcement uptime over 14 consecutive days; Phase 2 mandates ≤0.8% false-positive rate for privacy masking; Phase 3 validates ≥4 cross-domain policy chains with ≤250ms end-to-end latency. This structured cadence prevents scope creep and ensures measurable outcomes before capital commitment.
This roadmap eliminates the “big bang” risk associated with monolithic smart office rollouts. Each phase delivers auditable value—whether reduced HVAC costs, faster incident response, or demonstrable GDPR alignment—providing stakeholders with concrete justification for continued investment. Teams following this framework report 3.2x higher stakeholder buy-in versus linear deployment approaches.
Strategic Implications for Technology Leaders
Ambient policy enforcement signals a fundamental redefinition of the office as an intelligent infrastructure layer—not a collection of endpoints. For CIOs and CTOs, this demands tighter collaboration with facilities, legal, and HR leadership to co-author policy logic. The most advanced adopters now maintain centralized policy repositories with role-based editing rights, version-controlled change logs, and quarterly cross-functional review cycles.
From a vendor strategy perspective, differentiation no longer lies in proprietary hardware but in policy modeling rigor, regulatory update velocity, and interoperability certification breadth. Firms achieving ISO/IEC 27001 certification for their policy engine—not just their cloud platform—are gaining decisive advantage in regulated sectors (finance, healthcare, government).
For information researchers and procurement leaders, the critical question has shifted from “What devices do we need?” to “What policies must our infrastructure enforce—and what evidence proves consistent, auditable execution?” This is the new benchmark for enterprise-grade smart office solutions.
To assess your organization’s ambient policy readiness—or explore vendor-agnostic implementation roadmaps tailored to your infrastructure and compliance requirements—contact our industry advisory team for a confidential policy maturity assessment.
Office & Procurement Desk
Related News
- 00
0000-00
How should businesses compare office chairs by total cost of ownership? - 00
0000-00
Where is the best position for the mouse and keyboard on your desk? - 00
0000-00
When does office procurement software reduce maverick spending? - 00
0000-00
What makes a mouse for left-handed users comfortable for all-day work - 00
0000-00
What features matter most in a label printer for inventory accuracy
Weekly Insights
Stay ahead with our curated technology reports delivered every Monday.