Share
When in office communication systems need secure guest access
A visitor arrives early for a meeting, settles into a conference room, and asks for the Wi-Fi password. At nearly the same time, a contractor needs to connect a tablet to troubleshoot a display, while a candidate waiting in reception joins a video call from a personal laptop. None of these requests seems unusual. The problem begins when guest access is treated as a simple courtesy rather than a controlled connection to a working environment.
In office communication systems, the boundary between “visitor convenience” and “internal access” is often less visible than people expect. Smart displays, wireless presentation units, desk phones, conferencing bars, printers, shared tablets, and voice-enabled devices may sit on related networks or exchange information with internal services. A guest who receives an unrestricted password, scans an open device-discovery list, or plugs into an unused wall port may gain more visibility than intended. Even without malicious intent, unmanaged connections can cause interference, expose meeting information, complicate incident reviews, and leave teams unable to explain who accessed what.
Secure guest access is not necessary because every visitor is a threat. It becomes necessary when the office cannot confidently separate visitor activity from systems that support staff communication, business operations, or connected workplace devices. The practical question is not whether guests should be allowed online; it is when access must be limited, identified, time-bounded, and monitored.
The moment a guest connection becomes a security decision
Many workplaces begin with a basic guest network and assume the issue is solved. That arrangement can be adequate for a visitor who only needs ordinary internet access and whose device never interacts with local office equipment. It is not automatically adequate when guest activity touches communication workflows.
Secure guest access deserves closer attention in several common situations. One is a meeting room where external participants need to share content wirelessly. Another is a service visit involving a technician’s laptop, diagnostic tool, or mobile device. Offices that host interviews, training sessions, demonstrations, workshops, or client presentations also face a changing population of short-term users. Flexible workspaces increase the difficulty further: people may move between rooms, borrow peripherals, connect through docks, or use personal devices near systems intended for employees.
The issue also appears when consumer-electronics features enter the workplace. Devices designed for simple pairing and home-style convenience can make collaboration easier, but automatic Bluetooth discovery, screen casting, QR-code onboarding, voice control, and mobile companion apps can broaden the connection path. A feature that is harmless in a living room may require tighter governance in a room where confidential conversations, calendar details, or shared screens are present.
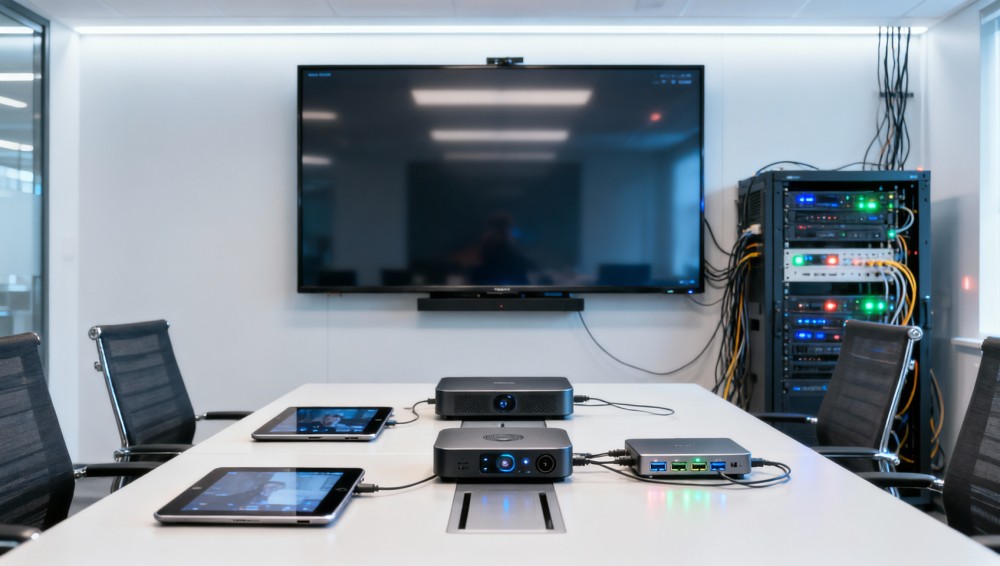
A useful trigger is this: if a guest device can discover, control, communicate with, or route through an internal asset, guest access should be designed rather than improvised. This includes more than the primary corporate network. It may involve wired ports, conference-room wireless systems, device setup networks, visitor tablets, temporary collaboration accounts, and remote-support connections.
Start by tracing the real connection paths
Before choosing controls, map what a guest can actually reach. Teams sometimes review the Wi-Fi name and password but overlook the rest of the room. A complete review follows the guest journey from arrival to departure.
Consider a typical meeting room. The visitor may receive a QR code for wireless access. They may then cast content to a display, join a video meeting, use a shared USB camera, connect to a charging station, or plug an adapter into a table-box port. Each action may use a different protocol and may be governed by different settings. If a room system is on the same accessible segment as internal workstations or management interfaces, the guest network label provides little assurance on its own.
Look for these conditions during the review:
- Guest wireless traffic can reach internal address ranges, device administration pages, network storage, printers, or collaboration appliances.
- Conference-room equipment accepts pairing requests from any nearby device without a room-specific approval step.
- Unused wired ports provide network access as soon as a cable is connected.
- Shared devices retain browser sessions, meeting credentials, contact lists, or downloaded files after a visitor leaves.
- A support provider needs temporary access but receives a standing account or unrestricted remote connection instead.
- Network logs identify only a shared password, making it difficult to distinguish one visitor session from another.
This mapping exercise often reveals that the main weakness is not a missing technology. It is an assumption: because a system is physically located in a meeting room, it is treated as separate from the rest of the office. Physical location does not determine network trust.
Separate access by purpose, not by who asks for it
A visitor requesting internet access, a presenter sharing a screen, and a technician servicing equipment do not need the same permissions. Combining those needs into one broad “guest” category creates unnecessary exposure and makes later review harder. A better approach assigns access according to the task being performed.
Internet-only visitor access should normally allow outbound internet use while preventing communication with internal systems and other guest devices where feasible. This is appropriate for visitors checking email, accessing cloud-based meeting links, or using ordinary web applications.
Presentation access may require connection to a designated room receiver or conferencing endpoint. It should be limited to that function. If the room system supports a one-time code, on-screen confirmation, or session-based pairing, these options reduce the chance that someone outside the meeting joins accidentally or reconnects later.
Service access is different. A technician may need to inspect a device, apply approved updates, or run diagnostics. That work can justify a controlled path to a specific asset, but it does not justify unrestricted movement across internal networks. The access should be limited to the named device or support gateway, active only for the maintenance window, and removed when the task ends.
Event access may need higher capacity and simpler onboarding, particularly when many external devices are expected. Even then, simplicity should not mean shared permanent credentials. A separate event network or time-limited invitation can preserve usability while avoiding a password that circulates indefinitely.
This purpose-based model is especially relevant to in office communication systems because those environments mix personal devices with shared endpoints. The goal is not to make every connection difficult. It is to ensure that an easy connection has a narrowly defined destination.
Controls that matter more than a guest password
A separate network name is a starting point, not the complete control set. Strong guest access usually depends on layers that work together. The exact implementation varies by network design, but the security intent should remain clear.
Network isolation and device isolation
Guest traffic should be separated from internal business traffic by network segmentation and rules that deny unnecessary routes. Equally important, guest devices should not automatically see each other. In a waiting area or training room, one visitor’s laptop has no normal reason to browse another visitor’s shared folders, discover media devices, or send traffic to nearby endpoints.
For connected meeting equipment, separate operational and management paths where possible. A display or conferencing device may need controlled communication with approved services, but its administration interface should not be exposed to every device that can join a room network. Management access should be restricted to authorized internal routes or dedicated support paths.
Time limits and individual accountability
Shared passwords are convenient until there is a problem. They are easily forwarded, rarely changed at the right time, and difficult to associate with a particular session. Individual credentials, sponsored invitations, temporary vouchers, or access codes with expiration dates provide better traceability. They also reduce the effort required to withdraw access after a meeting, event, or service visit.
Time limits should match the activity. A short meeting may need access for a few hours; a multi-day workshop may need a longer window. The important point is that access should not silently become permanent merely because nobody remembered to remove it.
Authentication proportional to the risk
Not every visitor needs a complex enrollment process. Requiring excessive identity verification for basic internet use can create queues and encourage staff to bypass the process. However, higher-risk activities deserve stronger confirmation. A guest who needs to administer a room device, use remote support, or access a restricted collaboration space should be authenticated in a way that is tied to the person and the approved task.
Approval should also be visible. If a room receiver accepts presentation requests, the person hosting the meeting should be able to see and approve the connection rather than allowing silent pairing from any nearby device.
Logging that can answer practical questions
Logging is useful only when it supports investigation and maintenance. At a minimum, records should help determine when a guest session started and ended, which access method was issued, which network or service was used, and whether a restricted connection attempt occurred. Privacy expectations and applicable internal rules should shape what is recorded and how long it is retained.
Do not treat logs as a substitute for prevention. Their value is in resolving uncertainty: Was an unfamiliar device connected during the meeting? Did a support session remain open? Was an access code used outside its intended window? Without meaningful records, these questions become difficult to answer.
A practical test before opening access to visitors
Configuration screens can look correct while the real user experience tells a different story. Testing should therefore resemble actual use. Use a non-privileged test device, not an administrator’s laptop, and attempt the same actions an ordinary visitor would attempt.
- Join the guest path. Confirm that onboarding works with the expected method, whether that is a temporary code, captive page, or approved invitation. Check that expired credentials no longer work.
- Try to reach internal resources. Attempt to open known internal web interfaces, discover nearby devices, and access shared services that should be unavailable. The expected result is denial, not merely a warning page.
- Test room collaboration separately. If wireless presentation is permitted, verify that the guest can connect only through the intended room workflow. Confirm that on-screen approval, session codes, or host controls behave as expected.
- Review wired connections. Test exposed meeting-room and reception ports. An inactive port should remain inactive; a port intended for visitors should follow the same isolation principles as guest Wi-Fi.
- End the session. Disconnect, let the access window expire, and confirm that the device cannot reconnect to the room system or retain access through a saved credential.
Repeat this test after major changes to wireless infrastructure, conferencing equipment, room-control software, or visitor onboarding processes. A replacement display, new docking station, or firmware update can alter discovery and pairing behavior without anyone intending to change the guest policy.
Where convenience quietly defeats the design
The most common failures are procedural. A staff member may share an internal wireless password because the guest portal is slow. A receptionist may keep an old event code active because it is easier than issuing new invitations. A meeting host may enable open casting to avoid delaying a presentation. These actions are understandable under time pressure, but they create exceptions that are rarely documented or reviewed.
Another weak point is the shared room device. A conferencing endpoint can retain meeting history, account tokens, Bluetooth pairings, cached files, or browser information. Guest access controls should therefore be paired with a reset routine. At the end of a meeting or at a scheduled interval, shared devices should clear temporary sessions and remove unneeded pairings. If a device cannot reliably clear such information, its intended use should be reconsidered.
Consumer-electronics features require particular attention here. Fast pairing, automatic reconnection, and companion-app control are designed to reduce friction. In a workplace, they should be enabled only when the connection can be bounded by room, session, or authorization. Leaving broad discovery active all day may make a device convenient for the next meeting, but it may also make it visible to the wrong person.
Deciding when stronger measures are justified
Basic isolated internet access may be sufficient for low-risk visitor use in a reception area. Stronger controls are justified when guests interact with internal communication endpoints, when confidential meetings occur, when a third party performs maintenance, or when the office relies heavily on shared connected devices.
Escalate the design when there is uncertainty about segmentation, repeated pairing issues, unexplained devices in logs, or equipment that cannot be updated and managed safely. In those cases, it may be necessary to involve network, facilities, and technology owners together. The communication system is often shared infrastructure: one group manages the room, another manages the network, and another owns the meeting service. Gaps tend to appear between those responsibilities.
Secure guest access works best when it is treated as part of normal room operation rather than an emergency restriction. A visitor should know how to connect, a host should know how to approve sharing, and temporary permissions should end without manual chasing. For in office communication systems, that balance protects operational reliability while keeping meetings and visitor interactions practical.
Technology Insights Desk
Related News
- 00
0000-00
Which customer service software features matter for omnichannel support? - 00
0000-00
How to measure ROI before adopting digital technologies - 00
0000-00
What is driving demand for smart equipment in the agri machinery industry? - 00
0000-00
What makes price monitoring data reliable enough for pricing decisions? - 00
0000-00
Choosing a business website builder with SEO tools that scales
Weekly Insights
Stay ahead with our curated technology reports delivered every Monday.